The Business Cost of Email Deliverability Failure
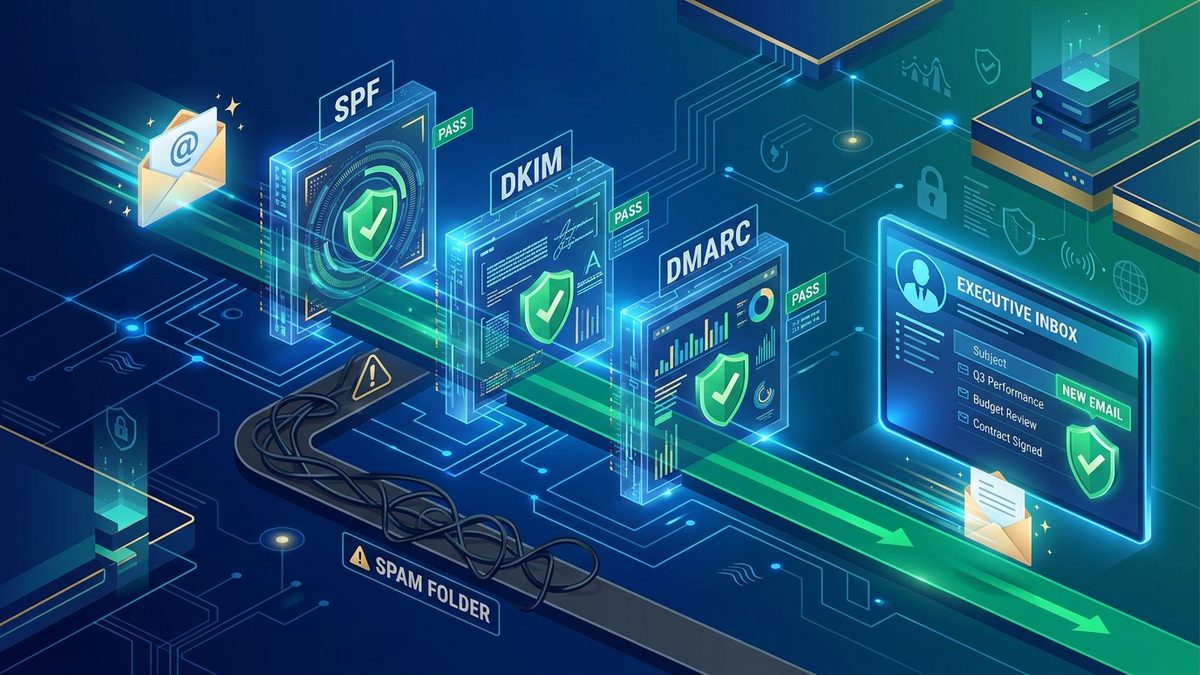
There is nothing more damaging to client communication than having business quotes, invoices, and sales proposals silently land in a customer's Junk or Spam folder. With email providers like Google Workspace, Microsoft 365, and Yahoo implementing strict enforcement rules, unauthenticated business domains face immediate delivery blocks.
Achieving 99%+ inbox placement requires configuring three interconnected DNS authentication protocols: SPF, DKIM, and DMARC.
1. Sender Policy Framework (SPF)
An SPF record tells recipient mail servers exactly which IP addresses are authorized to send mail from your domain name. A standard SPF TXT record looks like this:
v=spf1 include:_spf.titan.email include:spf.google.com ~all2. DomainKeys Identified Mail (DKIM)
DKIM creates a cryptographic public/private key pair. Your mail server signs outgoing emails with the private key, while recipient servers verify the signature using the public key published in your DNS records:
- Generate a 2048-bit DKIM key inside your cPanel, Titan, or Google Workspace dashboard.
- Publish the provided TXT record at your DNS host under the specified selector (e.g.,
default._domainkey.yourdomain.com).
3. Domain-based Message Authentication (DMARC)
DMARC ties SPF and DKIM together, instructing recipient servers how to handle emails that fail verification checks:
v=DMARC1; p=quarantine; rua=mailto:dmarc-reports@yourdomain.com; pct=100Start with a monitoring policy (p=none), analyze weekly aggregate reports, and gradually advance to p=quarantine or p=reject to permanently protect your domain against spoofing.