The Cybersecurity Regulatory Reality in India
Cybersecurity is no longer solely the concern of large banks and IT conglomerates. With cyber attacks, ransomware extortion, and website defacements surging across India, the Indian Computer Emergency Response Team (CERT-In) under the Ministry of Electronics and Information Technology (MeitY) has enforced strict cybersecurity directives across all Indian businesses.
Failure to comply with mandatory security logging and incident disclosure directives carries legal penalties under Section 70B(7) of the Information Technology Act 2000. Below is a practical, developer-friendly compliance roadmap for small and medium enterprises.
Core CERT-In Directives Every Website Owner Must Implement
- Mandatory 6-Hour Incident Reporting: Organizations must report security breaches, unauthorized server access, ransomware infections, and website defacements to CERT-In (incident@cert-in.org.in) within 6 hours of detection.
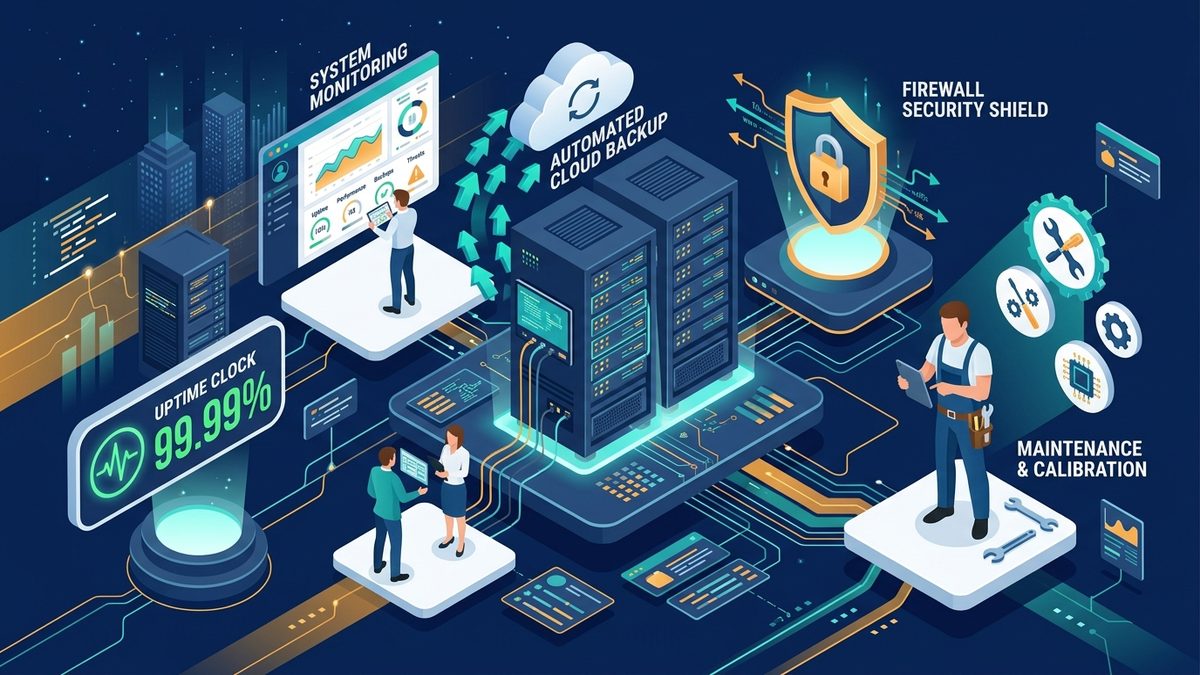
- NTP Server Synchronization: All server system clocks must be synchronized to official Indian Standard Time (IST) via National Informatics Centre (NIC) or National Physical Laboratory (NPL) Network Time Protocol (NTP) servers.
- 180-Day Secure Log Retention: Web servers (Apache/Nginx), firewalls, and database logs must be securely archived and retained within Indian sovereign jurisdiction for at least 180 consecutive days.
- Strict Data Privacy & Encryption: Enforce HTTPS encryption with TLS 1.3, disable deprecated SSL ciphers, and implement automated Web Application Firewalls (WAF) to block malicious SQL injection and Cross-Site Scripting (XSS) vectors.
Practical Server Hardening Steps for MSMEs
- Install a commercial Web Application Firewall (WAF) to filter malicious bot attacks and automated credential stuffing.
- Disable remote root SSH logins and enforce SSH key authentication on non-standard ports.
- Schedule automated off-site backups with immutable retention policies to ensure rapid recovery from ransomware attempts.
- Audit all website forms and API endpoints to ensure user data is encrypted at rest and in transit compliant with both CERT-In and the DPDP Act.